Zero Trust for Small Business.
Four branches went dark on a Thursday morning. The ISP had fingerprinted our VPN, so I spent the weekend rebuilding remote access on Zero Trust. Nothing was lost that a Monday would have noticed. Below is everything I kept: the case with transcripts, the narrative, the decision record, and the two stack notes.
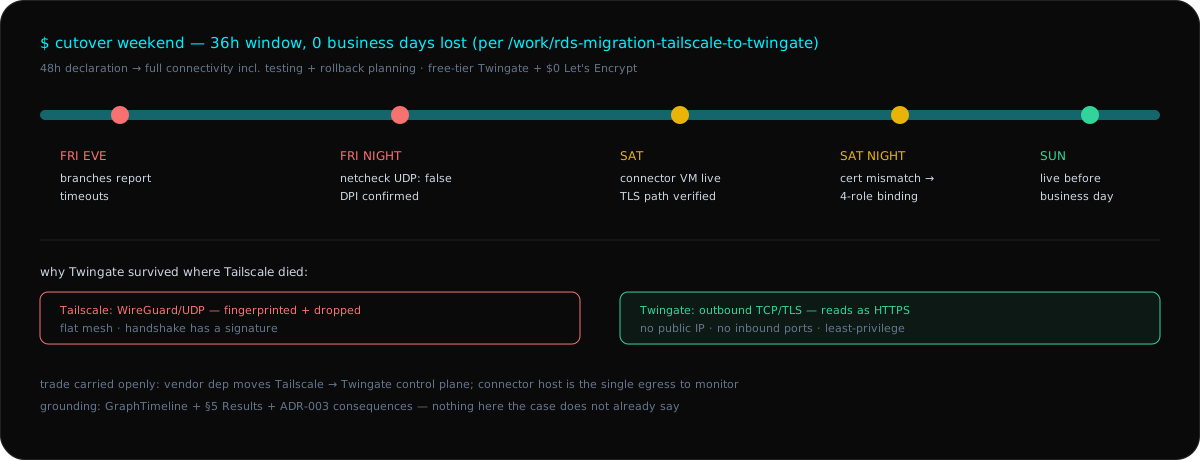
FRI EVE
branches report timeouts
FRI NIGHT
netcheck UDP: false — DPI confirmed
SAT
connector VM live — TLS path verified
SAT NIGHT
cert mismatch → 4-role binding
SUN
live before business day
~/guides/start-here
CASE · 36h window · 0 business days lost
Tally Prime Remote Access: Migrating RDS from Blocked Tailscale to Twingate
I kept the netcheck transcripts, the win-acme DNS-01 pipeline, the four-role binding script, and the cutover timeline.
NARRATIVE · 48h declaration-to-connectivity
Tailscale Blocked? Moving Tally Prime ERP to Twingate ZTNA
The Thursday-morning incident as it happened. The story version of the case above.
~/guides/the-decision
COMPARISON · verdict from ADR-003
Tailscale vs Twingate Under DPI: What Survived and Why
The protocol-shape table and the cutover metrics, with the trade stated plainly: vendor dependency moved, and the connector host is the egress I watch.
ADR · accepted 2025-10-26
Twingate ZTNA over Tailscale for RDS Remote Access
The decision record in my own words. Context, consequences, and the single-egress trade I accepted.
~/guides/the-hard-part
HOW-TO · the error-string-led fix
RDS Certificate Subject-Name Mismatch: Binding Let's Encrypt Across All Four Roles
The wall every RDS-behind-ZTNA migration hits. Then the 60-day-renewal script that holds it.
CONTEXT · the decade around the cutover
5 Lessons from 10 Years of Digital Transformation
Where the cutover sits in a ten-year arc. It includes the cost framework that keeps the $2,500 VPN saving distinct from the droplet saving.
~/guides/the-stack
STACK · phase-1 record · ~/uses Tailscale
Tailscale
The WireGuard mesh that carried the estate until DPI fingerprinted it. Honest about what it was good for, and where it died.
STACK · current fabric · ~/uses Twingate
Twingate
Outbound-TLS ZTNA with no public IP and no inbound ports. Nothing on the wire to fingerprint. Proved on the Oman cutover.
~/guides/next-steps
INTAKE · five outputs · migration sketch
What I Ask Before Touching Your VPN
Starting a migration of your own? Send five outputs (netcheck, DERP, cert names, NAT shape, rollback plan) and the sketch writes itself.
PLAN · phase 2 · the last hop
ZTNA Phase 2: Retiring the Last Fingerprintable Hop
The committed next step. What Phase 1 proved, and what the last legacy VPN segment still needs before I call it done.
Migrating something similar?
I led this cutover end to end: scope, migration, and guardrails. Tell me what you are running and I will reply with a migration sketch.